Wednesday, 18 November 202635 nodes21 stable releases in 7 dayscoverage 35/35 ok, checked 28 Oct 2026
dev/news
Release notes for 35 projects, from Rust and the BEAM to Anthropic and Mistral, read every day. The log keeps what changed, with the version, the date and the primary source.
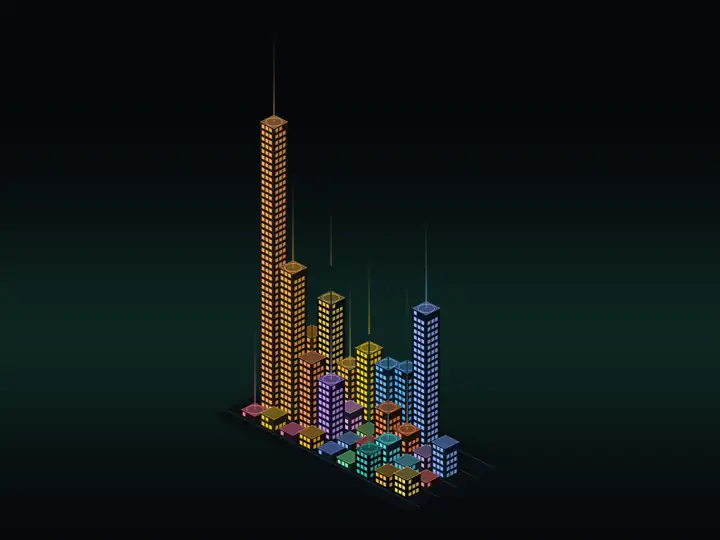
The network: one building per project, one lit window per stable release in the last 12 months (1309 in all). A beacon marks a release in the last 7 days.
1309stable releases across the network in 12 months
21stable releases in the last 7 days
11of 35 projects shipped this week
283from @cloudflare/workers-types, the busiest in 12 months
What needs action
As of , the entries below are the upgrades from to today where a stored stable release or a written log entry gives a reason to act, with the version, the date, and the identifier or change it names.
Security patches
If you maintain an Elixir deployment, check its minor line against the patches shipped on . Versions 1.20.5, 1.19.7, and 1.18.6 all address CVE-2026-109821 and CVE-2026-115274. Only 1.20.5 also names CVE-2026-97209.
The Hono advisory batches shipped in 4.13.16 on and 4.13.18 on . The notes for 4.13.16 name 5 advisories including GHSA-4m76-xfj5-7975. The notes for 4.13.18 name 5 advisories including GHSA-4h7h-rv7c-7m2v. Regenerate stored PreparedRegExpRouter data when updating Hono routes. Compare the version in your Hono lockfile with the latest stored stable, 4.13.19 on .
Check the patch level of each OCaml compiler line you distribute. 5.5.2 on lists 6 security identifiers, including OSEC-2026-21. 4.14.5 on lists 6 security identifiers, including OSEC 2026-24.
Toolchain and desktop
For Go toolchain updates, the announcement recorded on applies to 1.27.4 and 1.26.11. It counts 12 security fixes covering CVE-2026-97033 through CVE-2026-97043 plus CVE-2026-97054. Include the Go compiler on build hosts when checking deployed versions.
Visual Studio Code 1.145.3 on patched CVE-2026-102230 and CVE-2026-120780. The latest stored stable is 1.146.0 on .
The Docker Desktop patch history records a certificate change in 4.96.1 on and 4.96.2 and 4.96.3 on . Docker removed trust for the compromised eMudhra intermediate in batches as it updated components. Docker Desktop 4.97.0 on fixed CVE-2026-114409. Check Docker diagnostics bundles you already shared for cleartext credentials and sanitize or delete affected copies. Docker Desktop 4.98.0 on fixed CVE-2026-98432 and CVE-2026-112917. If you run 4.99.0 from , the certificate change and CVE fixes above are already in that release. Earlier Docker Desktop builds still need them.
Audit notes and pins
The Cargo Audit in Tauri 2.12.6 audit notes on lists allowed warnings. Check your lockfile for rustix 1.0.7, flagged as unsound, and compare it with the patched version 1.1.6.
A pin to an older Vite major still leaves a patch decision. On , Vite shipped 8.3.7, 8.2.6, 7.3.8, 8.1.7, and 6.4.6. Compare your Vite pin with the patch on its own line. Vite followed with 8.3.8 on .
For services pinned to Tokio LTS, match the deployed branch to its maintenance deadline. The LTS patches were 1.51.6 on for 1.51.x (supported through March 2027) and 1.53.3 on for 1.53.x (supported through September 2027). Tokio also shipped 1.54.1 on on the current line.
New minor lines
Rust 1.100.0 shipped on , 42 days after 1.99.0 opened the previous minor line. The notes list stabilization of the never type and custom allocators.
Diesel 2.4.0 shipped on , 427 days after 2.3.0 opened the previous minor line. Check the Diesel upgrade against queries that could use database views, a distinct MariaDB backend, and batch update statements.
When reviewing Zod 4.6.6 provenance from , distinguish the repository history from the published package. Zod reports that someone used a compromised git credential to push six malicious commits to main on September 21 and that the commits were reverted that day. None of those Zod commits reached npm. The latest stored Zod release is 4.6.7 on .
It is the tenth minor release since v2.0.0 on 21 October, one day after v2.9.0, and four of its five features are about billing: a beta billing_policy request parameter and three new error codes, among them contract_spend_limit_reached on messages. Anthropic Python SDK v2.10.0 release source
One tower per project, as tall as its stable releases since December 2025. @cloudflare/workers-types leads with 283; a green dot means a stable release in the last 7 days.
 Anthropic
 Wrangler